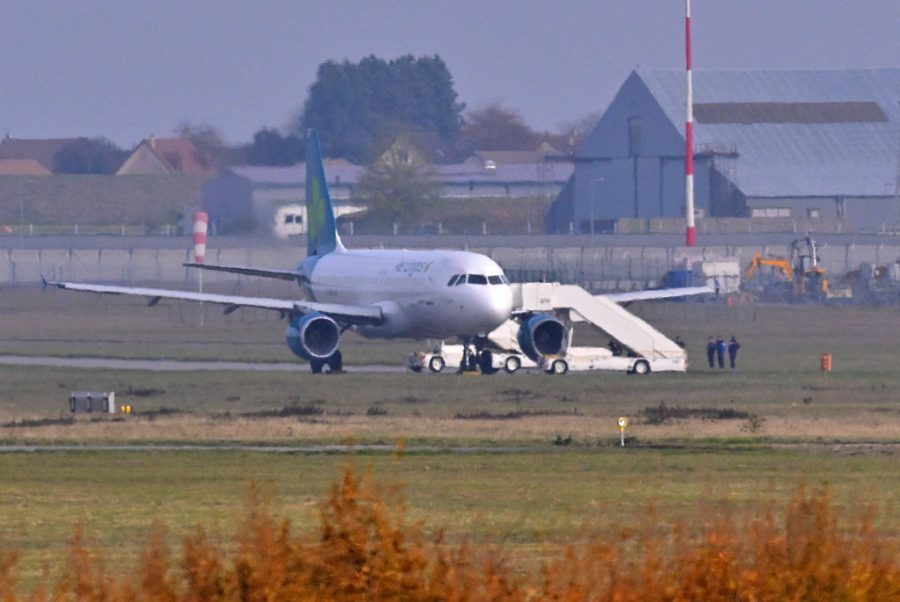
Earlier today, an Aer Lingus flight from Dublin to Rome was diverted to a French military airbase earlier following a bomb threat, while three Ryanair flights bound for Bulgaria were also targeted. This has happened amid a growing wave of bomb scares and cyberattacks disrupting essential infrastructure across Europe. So far, we do not know who or what is behind this wave of unconventional attacks, but their frequency is increasing.
The Aer Lingus aircraft, carrying 151 passengers and six crew, landed at Évreux military airbase in Normandy, where French military bomb-disposal teams were deployed. All aboard were reported safe. Of the three Ryanair flights travelling to Sofia, the service from London was diverted to Plovdiv, while those from Madrid and Copenhagen landed in the Bulgarian capital. These incidents follow seven bomb threats against European flights on Tuesday, affecting services to Poland, Italy, Spain and Bulgaria. A day earlier, a Wizz Air flight from London Luton to Sofia was diverted to Budapest under Hungarian fighter escort. On 18 October, an Austrian Airlines flight from Tel Aviv to Vienna was diverted to Sofia following another threat, with Bulgarian fighter jets scrambled.
No explosives were found in the earlier incidents. Yet aircraft were diverted, military jets deployed, airports disrupted and hundreds of passengers subjected to emergency procedures. On Tuesday, the Israeli-operated cruise ship Crown Iris was also evacuated in Greece after a bomb threat, with more than 1,500 passengers and crew affected.
Modern societies depend on an enormous network of interconnected systems
A different and potentially more troubling form of disruption has been simultaneously unfolding across Europe, equally mysteriously. Overnight cyberattacks on commercial refrigeration systems have affected supermarkets, food suppliers and warehouses in several countries, including Britain. In October, hundreds of French supermarkets were targeted after hackers remotely manipulated refrigeration controls, raising temperatures and extending defrost cycles. Tonnes of food were reportedly destroyed. A second wave on 2 November affected retailers across at least eight European countries. In Ireland, 13 SuperValu stores were hit. British meat suppliers and food wholesalers also reported compromised refrigeration systems. More disturbingly, three French blood-storage facilities had their temperature controls manipulated remotely, although staff intervened before any blood products were lost.
The vulnerability is remarkably mundane and has prompted plenty of people to roll their eyes over the idea of a fridge being connected to the internet in the first place. Such reactions miss the point entirely. Refrigeration systems are frequently connected to the internet for remote monitoring and maintenance. This is an entirely normal part of modern life, and to simply disconnect them all is not a solution. We enjoy levels of convenience and affordability previously unknown, thanks to the savings that such systems bring about.
But connectivity of the kind we have become accustomed to in the 21st century means these devices can become accessible to intruders, who may alter temperatures, disable alarms and interfere with equipment without physically coming into contact with them. There are usually protections in place against cyber attacks, but often they are not sophisticated enough, and if too much infrastructure relies on too few systems, one single weakness can cause widespread disruption across many locations and applications of the same technology. This is what these incidents reveal about the fragility of modern infrastructure.
An anonymous bomb threat can force a passenger aircraft out of the sky, mobilise fighter jets and close airport runways. A remotely accessed refrigeration controller can destroy a supermarket’s stock overnight, interrupt food distribution or threaten the integrity of blood supplies. The equipment may remain intact, but the disruption can still be extensive. In both cases, relatively limited actions can impose disproportionately large costs. Authorities cannot simply ignore a bomb warning because previous threats proved false. Food retailers cannot sell refrigerated products once their safety is uncertain. The precautions necessary to protect human life become part of the mechanism through which disruption is achieved.
There is currently no evidence establishing a connection between the aviation threats and refrigeration attacks. Nor do we know yet who was responsible. The incidents may ultimately prove unrelated, carried out by different perpetrators for entirely different reasons. But the coincidence raises a serious question about the changing nature of security threats in Europe. Modern societies depend on an enormous network of interconnected systems, from aviation and food distribution to hospitals, energy supplies and communications. Many are designed around efficiency, automation and remote access. Their reliability is assumed until something interferes with it. There are individuals, collectives and even state actors working hard to identify weaknesses and use them to cause mass disruption, or far worse.
So what happens when these vulnerabilities are exploited repeatedly, across different sectors and countries, without a conventional attack ever taking place? Such disruption could be an end in itself, designed to impose economic losses, exhaust security resources, spread uncertainty and gradually undermine public confidence in the systems on which daily life depends.
Our government can recommend we stock up on three days of water and food as much as it likes, but if our supermarkets and hospitals have unreliable refrigeration in the long term, a few tins of tuna or baked beans are not going to help us. Where is their coordinated security response to this kind of growing threat, to ensure we are properly protected as a nation? In a more dangerous scenario, all this could serve as preparation for a conventional conflict, exposing weaknesses, testing emergency responses and weakening a society’s capacity to withstand a more direct assault.
Neither explanation has so far been established in these cases. Both deserve consideration as Europe confronts the security implications of increasingly connected infrastructure. And these are only the cyber attacks we have heard of. Often, massive infrastructure failures are not declared as cyber attacks, when they might well have been. Many suspect that the authorities only admit a cyber attack when it is too wide-scale to deny it. In June 2024, a massive IT failure affected King’s College Hospital, Guy’s and St Thomas’, Royal Brompton and other London hospitals. Staff lost access to essential pathology systems, operations were cancelled, blood transfusions were disrupted and hospitals resorted to manual procedures. Initially, internal communications described a major IT incident. It was subsequently confirmed as a ransomware attack against Synnovis, the hospitals’ pathology provider. More than 11,000 appointments and procedures were delayed.
The disturbing possibility is that a country can suffer accumulating damage to its economy, essential services and public confidence long before anyone recognises that the disruption forms part of a broader campaign. And if these incidents are connected, the question becomes who is testing Europe’s vulnerabilities, and are we prepared to defend ourselves from them?


Comments